Read the audit log
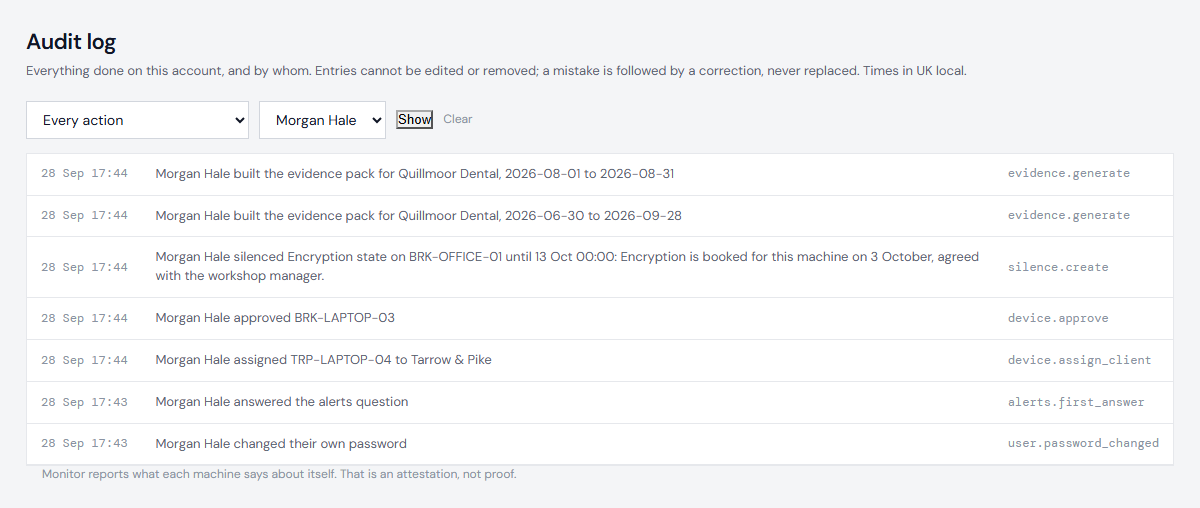
The audit log records who did what on your account, and when - newest first, each line a sentence, such as "Sam Owner silenced Firewall state on WS-04".
Open Audit. Anyone on your account can read it. Filter it by action, or by person.
What is recorded
- Machines approved, rejected, revoked, and moved between clients.
- Clients added, renamed, archived and restored.
- Logins added, disabled and re-enabled; passwords reset by an owner, and changed by their own user.
- Silences created and ended, with their reasons.
- A new enrolment code being made - never the code itself.
- Automatic updates switched on or off, and for what.
- People stopping and resuming their own alert emails.
- Anyone from our support team entering your account, marked as such.
What you can rely on
- Nothing in it can be edited or removed while your account is open, by you or by us. A mistake is followed by a correction, never replaced. When an account is closed and deleted, its audit log is kept apart for 6 years and then deleted: see Closing an account.
- It is written together with the change. An action that is not recorded did not happen, and a record always means the action did.
- It reads the same later. Each line keeps the names as they were at the time, so renaming a client or removing a login does not rewrite the past.
- Only real changes are recorded. Saving something as it already was writes nothing.
Next: Firewall requirements